Key Capabilities
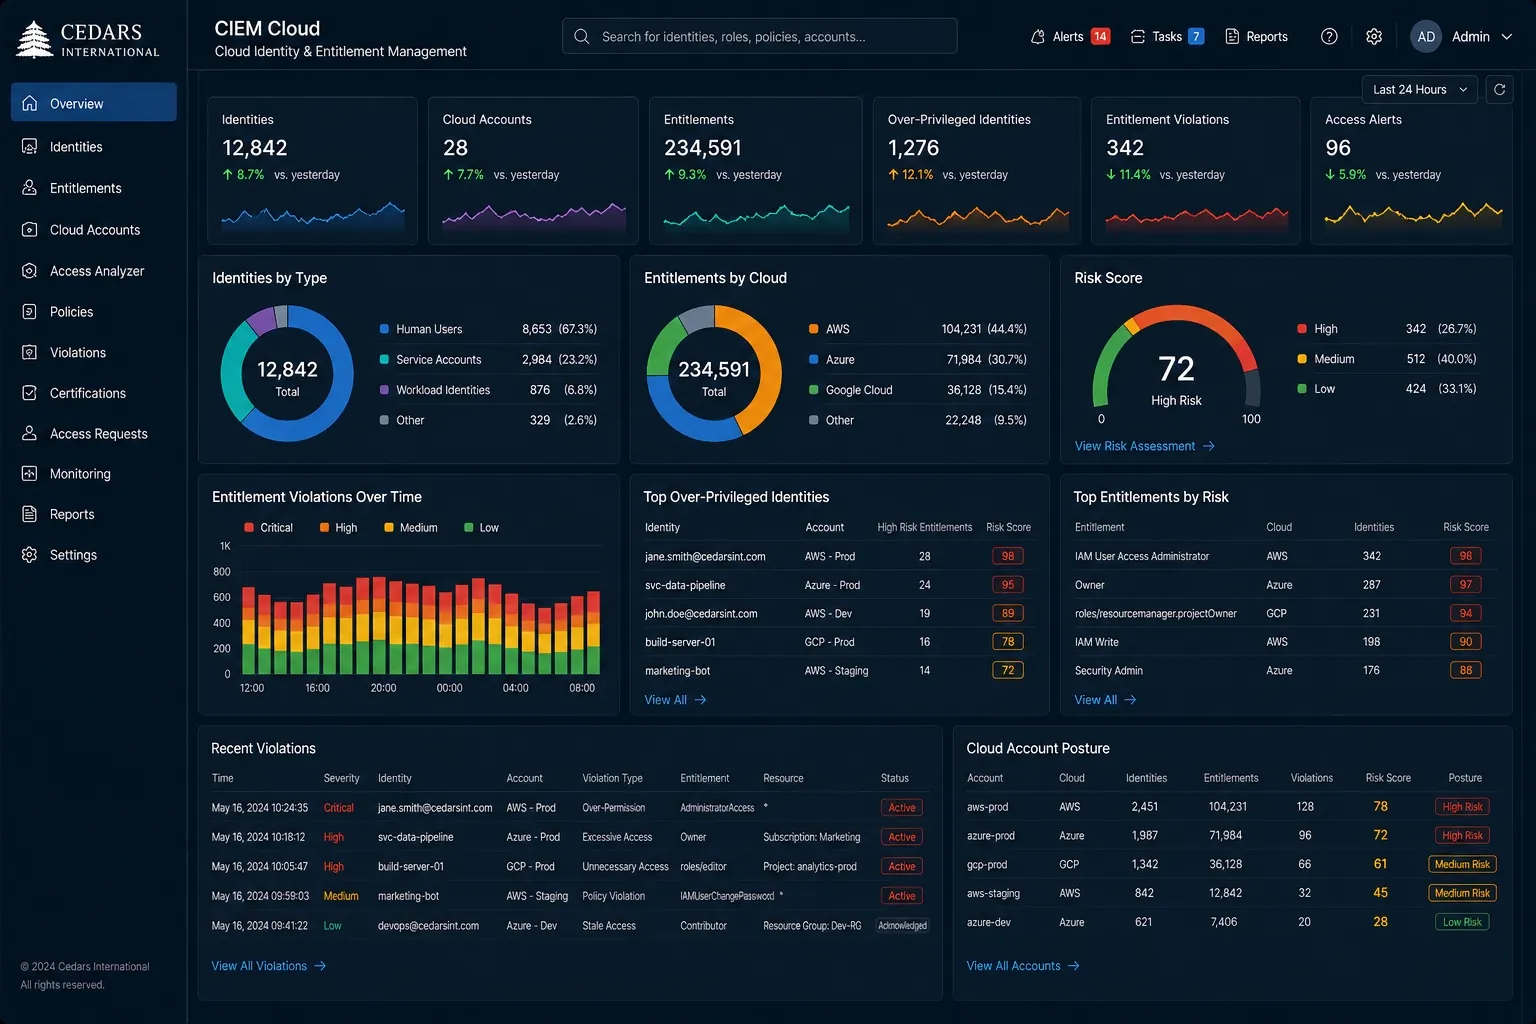
- • Multi-Cloud Permission Inventory — Automatically discovers and inventories all identities — users, roles, service accounts, federated identities — and their permissions across AWS, Azure, and GCP in one complete permission graph.
- • Over-Privileged Account Detection — Compares granted permissions against actual usage via cloud audit logs, flagging accounts where actual access is far less than granted access.
- • Permission Drift Monitoring — Alerts when permissions change — new policies attached, roles modified, admin access granted — in real time, with every change logged by who, when, and from what IP.
- • Least Privilege Recommendations — Generates specific, actionable remediation recommendations, such as removing unused permissions or revoking excess admin access.
- • Toxic Combination Detection — Identifies dangerous permission combinations that, when held by the same identity, create segregation of duties violations.
Security Impact
Cloud environments often accumulate excessive, unused, or conflicting permissions as teams, services, and infrastructure grow. These access rights can remain unnoticed and create opportunities for compromised accounts, insider threats, and privilege escalation.
CIEM Cloud gives security teams continuous visibility into cloud identities and permissions, helping them detect risky access, control permission changes, and enforce least privilege across multiple cloud platforms.
Business Outcomes
Reduce Excessive Access
Identify and remove unused or unnecessary permissions that increase the organization's cloud attack surface.
Prevent Privilege-Based Attacks
Detect over-privileged accounts, dangerous permission combinations, and unauthorized access changes before they can be exploited.
Improve Multi-Cloud Visibility
Manage identities, roles, service accounts, and entitlements across AWS, Azure, and Google Cloud from one centralized view.
Accelerate Access Reviews
Provide security and compliance teams with clear permission data, usage history, and recommended remediation actions.
Strengthen Compliance
Maintain detailed records of permission changes and demonstrate consistent enforcement of access-control and least-privilege policies.
Reduce Permission Debt
Continuously identify and correct access risks before excessive permissions accumulate across cloud environments.
How It Works
Modern cloud environments accumulate thousands of IAM roles, policies, and entitlements that grow in complexity with every new service, team member, and project. Without continuous monitoring, organizations develop "permission debt" — excessive access rights that create massive attack surfaces, where a single over-privileged service account can be the entry point for a catastrophic breach. CIEM Cloud feeds identity risk signals into CCDS — over-privileged accounts are flagged in Cedars SIEM for enhanced activity monitoring, and critical permission changes trigger CedarsTI to check for associated threat actor activity.
Ready to get started?
Contact us to get more information or schedule a quick demo