Turn Security Data Into Faster Decisions
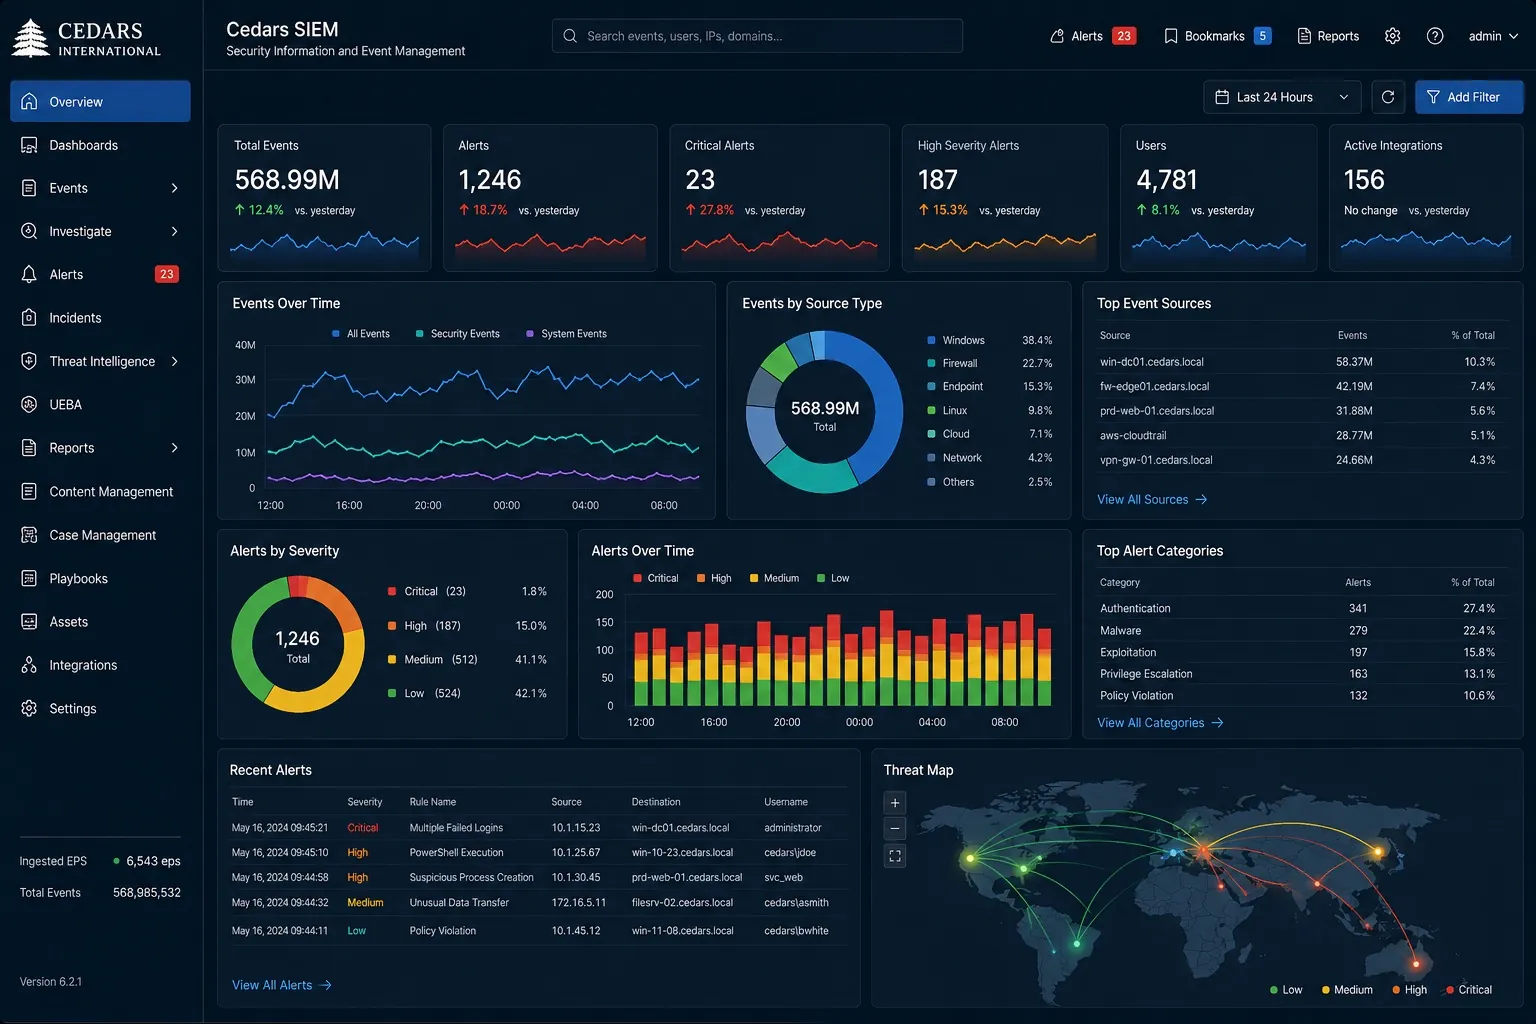
Cedars SIEM brings security events from across your organization into one clear, centralized view. It helps security teams identify suspicious activity earlier, investigate incidents faster, and respond before threats create serious operational or financial damage.
Business Value
One Platform, Greater Visibility
As part of the Cedars Cyber Defense Shield, Cedars SIEM can connect security monitoring with asset visibility, threat intelligence, vulnerability management, incident response, compliance, and case management. This gives organizations a more complete understanding of their security posture and helps teams coordinate their response from detection through resolution.
Key Capabilities
- • AI-Powered Log Parsing — The system learns each log source format automatically, with no manual parsing rules needed.
- • Automated Incident Timeline — Every incident gets a chronological event timeline, an assigned owner, an SLA countdown, and PDF export.
- • MITRE ATT&CK Heatmap — The dashboard shows which tactics and techniques are currently active across your environment.
- • Elasticsearch Analytics — Real-time search and aggregation across millions of log events with sub-second response.
- • Cross-Module Integration — Incidents automatically trigger alerts in ShadowGuard, CTI, GRC, and Awareness via CCDS's N:M correlation matrix.
How It Works
Agents run as background services on endpoint machines, collecting system logs, authentication events, process activity, and network connections every five minutes. Raw logs from any source — Windows Event Log, Linux Syslog, APIs, or cloud — are normalized into a unified format, and AI-powered parsing automatically extracts entities such as IP addresses, usernames, file hashes, and domains. Administrators define detection rules combining logical operators that auto-create prioritized incidents when conditions are met, each one automatically tagged with relevant MITRE ATT&CK tactics and techniques. Detected entities and their relationships are visualized as an interactive network graph, letting analysts trace attack paths visually — and incidents automatically trigger alerts across ShadowGuard, CTI, GRC, and Awareness via CCDS's N:M correlation matrix.
Ready to get started?
Contact us to get more information or schedule a quick demo