Core Capabilities
- • CVE Scanning & Tracking — Continuously scans your infrastructure against the National Vulnerability Database and other CVE sources, enriching each finding with CVSS score, exploit availability, affected assets, and time-to-patch metrics.
- • Pentest & SAST/DAST Integration — Imports findings from popular pentest tools and CI/CD SAST/DAST pipelines, deduplicating, correlating, and prioritizing everything in one unified view.
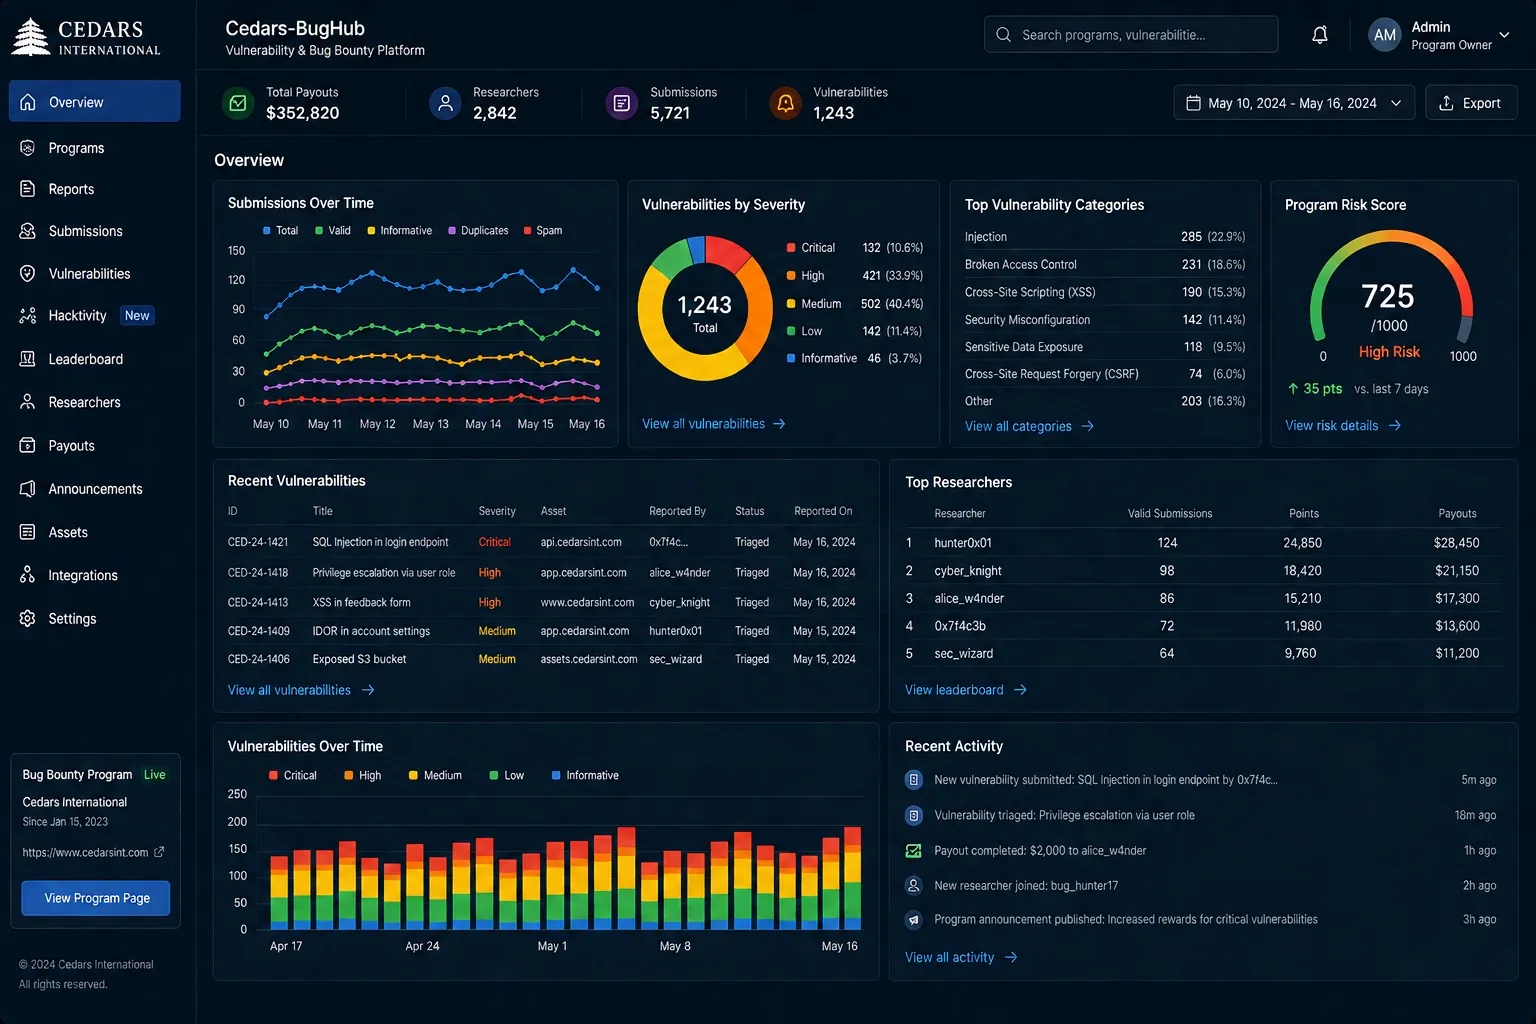
- • Bug Bounty Management — Manage your bug bounty program directly from BugHub — receive researcher submissions, triage findings, communicate with researchers, and maintain a full audit trail.
- • Exploit Availability Tracking — Monitors exploit databases and flags when a public exploit becomes available for a vulnerability in your environment, immediately escalating priority.
- • Prioritized Remediation Dashboard — Ranks findings by a composite risk score combining CVSS severity, exploit availability, asset criticality, and exposure level, so your team knows exactly what to fix first.
- • Patch Management Integration — Tracks patch status for all findings from identified through in progress to verified fixed, with SLA tracking and overdue alerts.
Security Impact
Vulnerability data is often scattered across scanners, pentest reports, development pipelines, and bug bounty programs. Without a unified view, critical findings can be duplicated, overlooked, or delayed while security teams spend time deciding what to address first.
Cedars-BugHub centralizes vulnerability information and prioritizes findings based on real-world risk, helping teams identify the most urgent issues, coordinate remediation, and reduce exposure before vulnerabilities can be exploited.
Business Outcomes
Focus on the Highest-Risk Vulnerabilities
Prioritize findings using severity, exploit availability, asset criticality, and exposure instead of relying on CVSS scores alone.
Reduce Vulnerability Backlogs
Consolidate and deduplicate findings from multiple sources, giving teams one clear remediation queue.
Accelerate Remediation
Track each vulnerability from discovery to verified resolution, with ownership, status, SLA monitoring, and overdue alerts.
Improve Coordination Across Teams
Give security, IT, and development teams a shared view of vulnerabilities, remediation priorities, and progress.
Respond Faster to Emerging Exploits
Automatically raise the priority of vulnerabilities when public exploits become available or active exploitation is detected.
Strengthen Reporting and Accountability
Maintain a complete audit trail of findings, decisions, remediation activity, and verification for internal reporting and compliance reviews.
Integration with CCDS
Critical vulnerabilities in BugHub automatically trigger alerts in Cedars SIEM, to watch for exploitation attempts, and CedarsTI, to check if exploits are being actively used in current threat campaigns.
Ready to get started?
Contact us to get more information or schedule a quick demo