Key Capabilities
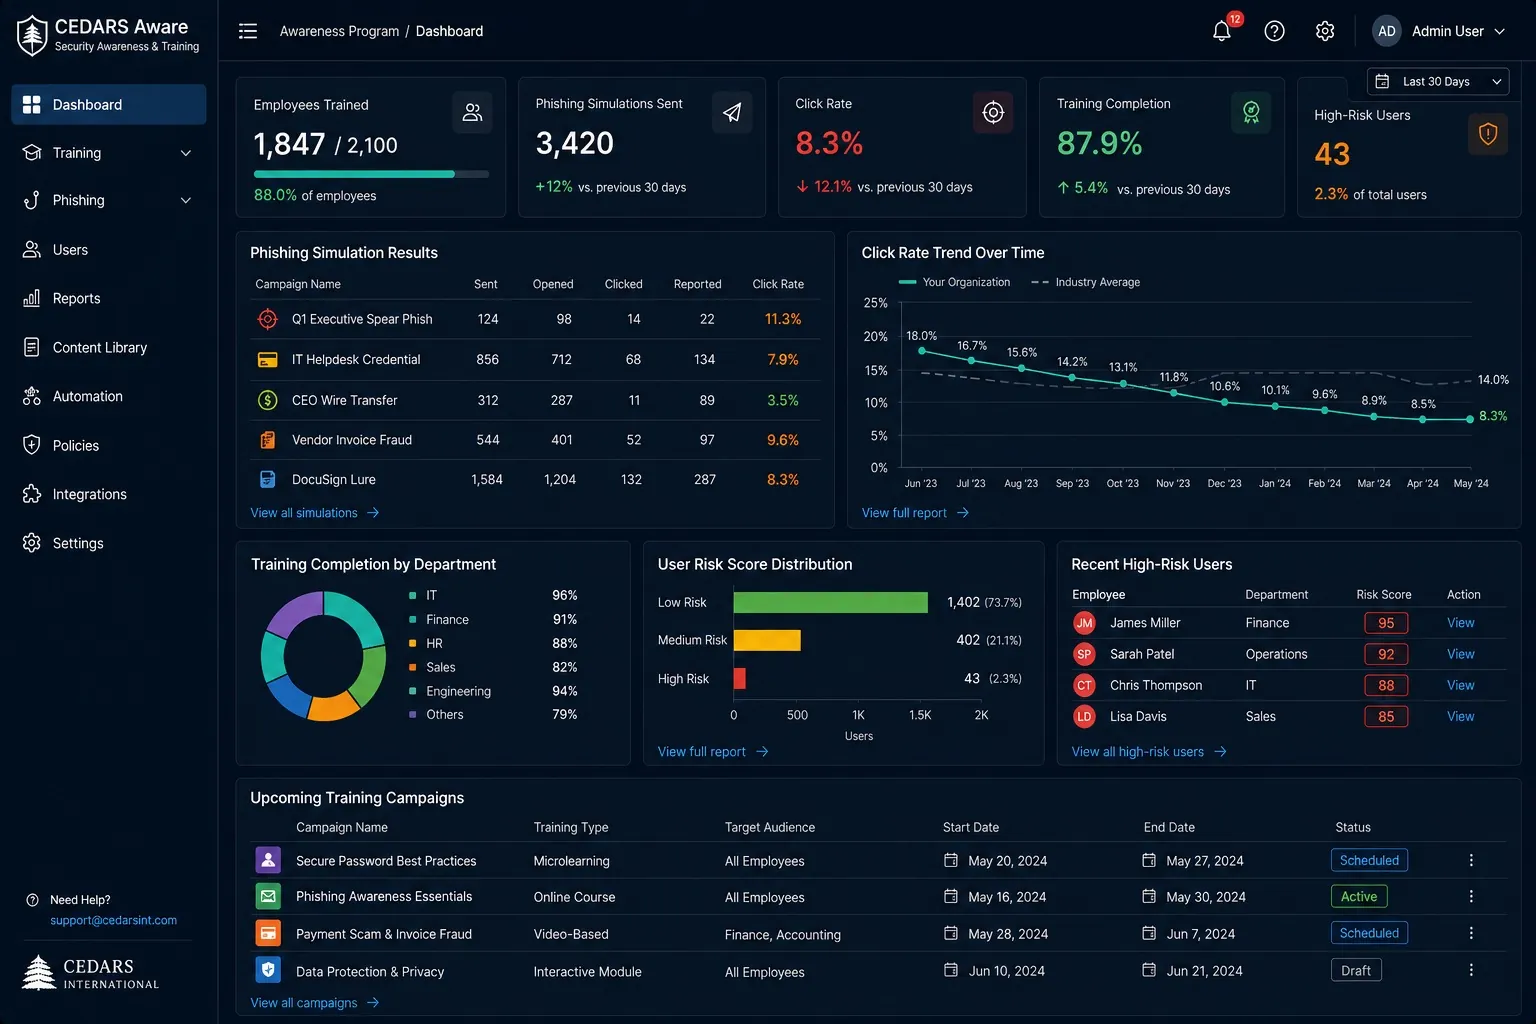
- • Phishing Simulations — Launch realistic phishing campaigns from a continuously updated template library — credential harvesting, malware delivery, executive impersonation, invoice fraud — and track who clicked, submitted credentials, or reported the email.
- • Interactive Training Modules — Assign targeted e-learning courses based on each employee's risk profile and simulation results, covering phishing recognition, password hygiene, social engineering, data handling, device security, and incident reporting.
- • Real-Time User Risk Scoring — Every user gets a dynamic risk score based on simulation performance, training completion, policy acknowledgments, and repeat offense history, automatically flagging high-risk users for remediation training.
- • Automated Campaign Scheduling — Runs recurring phishing campaigns with automatic difficulty progression — harder simulations for users who consistently spot phishing, targeted remediation content for those who fall for it.
- • Compliance Reporting — Generates training completion reports for ISO 27001, GDPR, NIS2, and other frameworks, tracking completion rates by department, role, and location.
Security Impact
Human error remains a major source of security risk. Phishing, social engineering, weak password practices, and improper data handling can give attackers access even when technical security controls are in place.
Cedars-Aware helps organizations reduce this risk through continuous training, realistic simulations, and user-level risk monitoring. It enables security teams to identify vulnerable users, provide targeted education, and build stronger security awareness across the organization.
Business Outcomes
Reduce Human-Related Security Risk
Train employees to recognize phishing, social engineering, credential theft, and other common attack methods.
Identify High-Risk Users
Use simulation results, training completion, and repeat behavior to identify employees who require additional support or remediation.
Improve Phishing Resilience
Test employees with realistic phishing scenarios and measure how effectively they recognize, avoid, and report suspicious messages.
Deliver Targeted Training
Assign relevant training based on each employee's role, risk score, and previous simulation results.
Strengthen Security Culture
Make security awareness an ongoing process rather than a one-time annual training requirement.
Support Compliance Requirements
Track training completion, policy acknowledgment, and campaign results to support audits and regulatory reporting.
Measure Improvement Over Time
Monitor employee risk scores, reporting rates, simulation performance, and training progress across teams and departments.
Integration with Cedars SIEM
When Cedars-Aware detects a user who clicked a phishing simulation and submitted credentials, it signals CedarsTI to check if that user's credentials appear in any breach databases, Cedars SIEM to increase authentication monitoring for that account, and ImperionGRC to log the incident in the compliance risk register.
Ready to get started?
Contact us to get more information or schedule a quick demo